Imagine running a busy ecommerce website when suddenly, hundreds of suspicious requests start hitting your login page. Your server begins slowing down, security alerts pile up, and legitimate customers struggle to access their accounts.
Not exactly the experience you want visitors to remember.
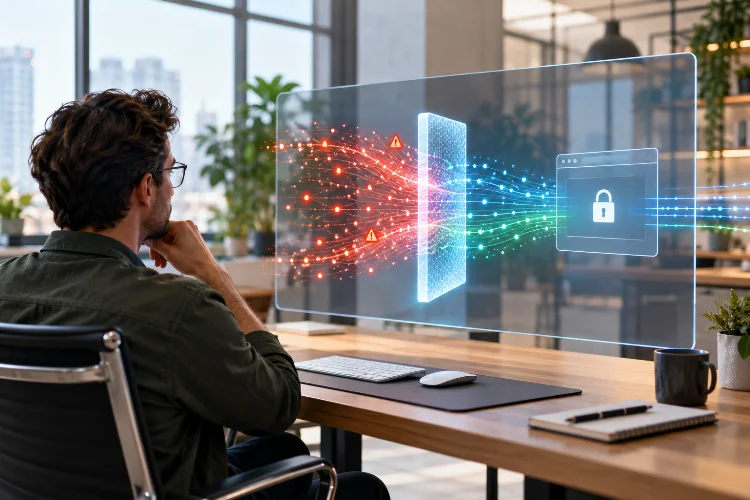
A Web Application Firewall (WAF) can help prevent situations like this by inspecting incoming HTTP traffic and filtering requests that match suspicious or malicious patterns.
But there’s a catch.
Simply enabling every available security rule isn’t necessarily the smartest approach. Overly aggressive configurations can block real customers, interfere with payment processing, or break essential website features.
That’s why designing web application firewall rules for managed hosting requires a balance between security and usability.
The goal is to block harmful requests while keeping normal website activity running smoothly.
Fortunately, modern managed hosting platforms and cloud security providers offer managed rule collections, custom filtering, rate limiting, and monitoring tools that simplify the process.
In this guide, we’ll explore how to build practical WAF policies, prevent common web attacks, reduce false positives, and maintain effective protection without creating unnecessary headaches for website visitors.
1. Understanding How WAF Rules Protect Managed Hosting Environments
A Web Application Firewall operates at the application layer, inspecting HTTP and HTTPS requests before they reach protected web applications.
Unlike traditional network firewalls that primarily control network connections, WAFs analyze application-level information such as request paths, headers, cookies, query parameters, and supported request bodies.
This makes them useful for detecting suspicious interactions with web applications.
What Threats Can a WAF Help Prevent?
Web applications face several common attack categories.
SQL injection attempts target unsafe database interactions, while cross-site scripting (XSS) attacks exploit weaknesses in how applications process or display untrusted content.
Other threats include malicious file requests, unauthorized access attempts, suspicious bots, and certain forms of automated application abuse.
A WAF can identify many recognizable attack patterns and take action before requests reach the backend server.
For example, a managed WordPress website might receive repeated requests targeting known vulnerable plugin endpoints.
A properly configured WAF can reject matching requests while allowing ordinary visitors to continue browsing.
However, WAFs aren’t guaranteed to identify every attack. Business logic vulnerabilities and authorization problems still require secure application design.
Why Managed Hosting Needs a Different Approach
Managed hosting providers typically handle some infrastructure administration, including server maintenance, operating system updates, or platform-level security controls.
This reduces operational work for website owners.
However, customers may have limited access to underlying server configurations.
Depending on the hosting provider, WAF settings might be available through a control panel, a CDN integration, or a separate cloud security service.
Some providers manage most filtering rules internally and allow only a limited selection of custom policies.
Before designing your security rules, identify which controls your hosting plan actually provides.
Understanding those limitations prevents spending time planning configurations that can’t be implemented on your platform.
2. Start With Managed WAF Rules and Proven Security Baselines
Building every security rule manually sounds flexible, but it isn’t usually the best starting point.
Attack patterns evolve constantly, and maintaining thousands of detection signatures requires specialized expertise.
Managed rule collections simplify this responsibility.
Use Managed Rule Sets for Common Threats
Cloudflare, AWS WAF, Azure WAF, and other security platforms provide managed rule sets designed to detect common application threats.
These collections may include protections against known vulnerabilities, suspicious request patterns, and common exploitation techniques.
The Cloudflare Managed Ruleset documentation explains that its rules are updated regularly and that some rules remain disabled by default to balance protection against false positives.
This is an important distinction.
Enabling every possible rule without testing can interfere with legitimate website traffic.
Instead, begin with the provider’s recommended baseline and enable additional protections according to your application technology.
For example, a WordPress website may benefit from relevant WordPress-specific protections, while an API-focused application requires attention to request methods, authentication endpoints, and JSON payloads.
Understand the OWASP Core Rule Set
The OWASP Core Rule Set (CRS) is a widely recognized collection of generic attack-detection rules for compatible web application firewalls.
It helps identify categories such as SQL injection, cross-site scripting, and other common attacks against web applications.
One interesting feature is anomaly scoring.
Rather than immediately blocking every request that matches a suspicious pattern, CRS can assign scores to individual rule matches.
According to the OWASP CRS anomaly scoring documentation, rules have different severity levels that contribute to an overall anomaly score.
For example, a critical rule match has a default score of five, while a warning-level match contributes three.
The final enforcement decision depends on the configured anomaly threshold and other relevant settings.
This gives administrators flexibility when balancing security and usability.
Adjust Security Sensitivity Gradually
More aggressive detection settings can identify additional suspicious requests, but they may also increase false positives.
Imagine a programming education website where students submit legitimate code samples.
Some submissions might resemble injection attempts, even though they’re part of normal educational activities.
Blocking every matching request could make the website unusable.
Start with reasonable detection sensitivity, monitor suspicious events, and increase protection gradually when evidence supports doing so.
A carefully tuned baseline is more useful than an overly aggressive policy that constantly interrupts visitors.
3. Create Custom WAF Rules Around Your Website’s Real Risks
Managed rules provide broad protection, but every website has its own sensitive endpoints and traffic patterns.
Custom WAF rules let administrators address those specific needs.
The key is creating targeted conditions instead of applying broad restrictions across the entire website.
Protect Login and Administration Pages
Login forms and administrative interfaces are common targets for automated abuse.
A practical custom rule could focus on requests reaching /wp-login.php, /admin/login, or another genuine authentication endpoint.
Rather than blocking everyone accessing the page, the rule could combine request paths with rate limiting or suitable challenge mechanisms.
For example, a Cloudflare custom rule can match a WordPress login path using an expression such as:
http.request.uri.path eq "/wp-login.php"
This expression identifies matching requests; the chosen security action determines what happens next.
The Cloudflare custom rules documentation explains how administrators can create expressions and select actions through the dashboard.
Remember that restricting administrative pages by IP address may be impractical when employees work remotely or use changing connections.
Where possible, combine WAF protection with strong authentication and multifactor authentication.
Choose the Right Security Action
Not every suspicious request deserves an immediate block.
Different WAF actions are appropriate for different levels of confidence.
| WAF Action | Purpose | Typical Use |
|---|---|---|
| Block | Reject matching traffic | High-confidence malicious requests |
| Challenge | Require additional verification | Suspicious automated activity |
| Log or Count | Observe matches without blocking | Testing new rules |
| Skip or Exception | Exempt specific traffic from selected checks | Verified false positives |
Available actions vary across providers and subscription plans.
Some platforms also support JavaScript challenges, managed challenges, CAPTCHA, or additional bot-detection mechanisms.
Use blocking for requests that clearly violate established security policies.
For uncertain activity, monitoring or adaptive challenges may be more appropriate.
Pay Attention to Rule Evaluation Order
Rule priority can influence which protections actually run.
For example, AWS WAF evaluates rules according to configured numeric priorities, and certain actions terminate further evaluation.
A broad allow rule placed too early could prevent later security rules from inspecting matching traffic.
The AWS WAF rule priority documentation explains how evaluation order affects request handling.
Different providers use different processing phases and action semantics, so don’t assume one platform’s rule behavior applies everywhere.
Review the complete policy before introducing new exceptions or changing priorities.
4. Configure Rate Limiting to Reduce Bots and Automated Abuse
A large percentage of unwanted web traffic comes from automated clients.
Not all bots are malicious, of course. Search engine crawlers, monitoring services, and legitimate integrations also make automated requests.
The challenge is distinguishing acceptable automation from activity that places unnecessary pressure on your application.
Apply Rate Limits to Sensitive Endpoints
Rate limiting restricts how frequently matching requests can be made within a defined period.
This can help protect login forms, account recovery pages, registration endpoints, and expensive API operations.
Imagine a website where normal users rarely submit more than five login attempts within one minute.
A rate-limiting policy might begin additional verification after an unusually high number of attempts.
However, the ideal threshold depends on actual traffic behavior.
A hypothetical limit of 30 requests per minute from one IP address might be reasonable for one endpoint and completely inappropriate for another.
The Cloudflare rate limiting documentation describes how request characteristics, counting periods, and matching conditions influence enforcement.
These options may differ depending on the provider and hosting plan.
Avoid Blocking Shared Networks
IP-based rate limiting has limitations.
Many legitimate users can share one public IP address through corporate networks, universities, or mobile network address translation.
A strict per-IP rule might incorrectly treat their combined activity as suspicious.
Where supported, consider additional characteristics such as authenticated identity, validated API credentials, or provider-generated visitor identifiers.
Be careful with client-provided headers because untrusted values can be spoofed.
A reliable rule should use characteristics the security platform can authenticate or verify.
Protect APIs Without Breaking Integrations
Application APIs often behave differently from ordinary browser sessions.
A legitimate inventory integration might send hundreds of requests during a synchronization process.
Applying the same rate limits used for a consumer login form could interrupt that integration.
Create seperate policies for public APIs, authenticated integrations, and administrative endpoints.
Use endpoint-specific thresholds based on observed traffic and business requirements.
Sensitive operations should also implement authentication, authorization, and application-level protections.
A WAF helps filter abuse, but it shouldn’t become the only control determining who can access valuable data.
5. Reduce False Positives Without Weakening Website Security
False positives are one of the most frustrating parts of managing a WAF.
They occur when security rules identify legitamate requests as malicious.
A customer might be blocked while submitting a checkout form, uploading a document, or saving an ordinary profile update.
These incidents can damage the user experience and potentially affect revenue.
Begin With Detection or Monitoring Mode
Before enforcing new protections, observe how they behave with normal traffic.
AWS WAF supports Count actions, while Azure WAF provides a detection mode that records rule matches without actively blocking requests.
Some Cloudflare configurations offer logging actions, although availability depends on the plan.
The Azure WAF best practices guide recommends using detection mode while tuning rules before moving to prevention mode.
This approach helps identify legitimate interactions that might otherwise be interrupted.
However, monitoring modes don’t provide the same protection as active blocking, so they should be used as part of a controlled rollout.
Create Narrowly Scoped Exceptions
Suppose your website allows customers to submit technical documentation containing code snippets.
A managed rule might occasionally flag these submissions as suspicious.
The wrong solution would be disabling all injection protections across the website.
A better approach is identifying the specific rule, endpoint, and request conditions responsible for the false positive.
Then create an exception that affects only the necessary traffic.
For example, you might exempt one specific managed rule from a particular authenticated content-submission endpoint while leaving all other protections active.
Cloudflare’s managed rule troubleshooting guidance recommends targeted exceptions rather than unnecessarily disabling entire rulesets.
Always verify that exceptions don’t create obvious opportunities for unauthorized requests.
Test Important User Journeys
Security testing should include normal website activities, not just simulated attacks.
Check account registration, login, checkout, search, file uploads, password recovery, and administrator workflows.
For managed ecommerce websites, verify that payment providers and fulfillment integrations continue working.
A technically successful WAF deployment isn’t useful if customers can’t complete purchases.
Repeat these tests after major application changes or managed rule updates.
6. Monitor WAF Performance and Deploy Changes Safely
A WAF requires ongoing attention to remain effective.
New vulnerabilities appear, applications change, and legitimate traffic patterns evolve.
Without monitoring, administrators may not realize that a rule is ineffective or unintentionally blocking important requests.
Track Meaningful Security Metrics
Start by monitoring total requests, blocked requests, challenged requests, and rule matches.
Look for unusual changes rather than treating every blocked request as a confirmed attack.
A sudden increase in blocked traffic might indicate malicious activity, but it could also reflect a new rule causing false positives.
For example, imagine your website processes 100,000 requests daily.
After introducing a rule, 4,000 requests are blocked instead of the previous 500.
That increase deserves investigation.
Review matching endpoints, request characteristics, geographic patterns, and available application logs.
Also monitor checkout completion rates, login success, API error rates, and customer support reports.
Security events and business metrics together provide a more complete picture.
Use a Controlled Deployment Process
Treat WAF policies like application configurations.
Before implementing a rule, document its purpose, expected traffic matches, chosen action, and rollback procedure.
Test it in a staging environment when practical.
Then observe production matches without blocking where the provider supports that workflow.
Once you’ve confirmed acceptable behavior, gradually enable enforcement.
Avoid making numerous unrelated rule changes simultaneously.
When several protections change at once, identifying the source of an unexpected problem becomes considerably harder.
Infrastructure as Code can also help maintain a consistent configuraton across supported environments.
Protect Logs and Monitoring Data
WAF logs may contain IP addresses, URLs, request metadata, and sometimes sensitive information.
Logging systems should follow appropriate retention, access control, and data protection requirements.
Avoid capturing full authentication tokens, passwords, or unnecessary personal information.
Limit access to security events and use appropriate redaction features when available.
Monitoring should help investigate threats without creating another source of sensitive data exposure.
7. Build a Long-Term WAF Strategy for Managed Hosting
A strong WAF deployment isn’t the one with the largest number of rules.
It’s the one that protects critical application functions while remaining understandable, measurable, and practical to maintain.
This becomes particularly important when managed hosting customers have limited control over the underlying infrastructure.
Coordinate With Your Hosting Provider
Before introducing additional WAF services, review the security features already included in your hosting package.
Some providers operate platform-level firewalls, intrusion prevention systems, or managed ModSecurity rules.
Adding another WAF at the CDN layer can improve protection, but overlapping configurations may complicate troubleshooting.
For example, a request might pass through a CDN WAF successfully and then get rejected by the hosting provider’s internal security system.
When investigating a blocked request, determine which layer generated the response.
Also consider protecting your origin server from unintended direct access when your hosting architecture supports it.
If attackers can bypass the edge WAF and reach the origin directly, some perimeter protections may lose effectiveness.
Balance Security, Performance, and Cost
Advanced WAF features can introduce additional subscription expenses.
Managed rule packages, bot detection, request inspection, and high-volume logging may have different pricing structures.
A small content website may not need every enterprise security feature.
An ecommerce platform handling customer accounts and payment-related workflows may justify more comprehensive protection.
Evaluate security spending against exposure, application sensitivity, and actual operational requirements.
Also monitor performance, since challenges, additional processing, and incorrectly configured rules can affect legitimate visitors.
Security should reduce business risk without creating unecessary friction.
Review Your Rules Regularly
Set a recurring schedule for reviewing WAF policies.
Remove outdated exceptions, investigate rules that never match traffic, and reassess rate limits as visitor activity changes.
Check whether newly introduced application endpoints require additional protection.
Pay particular attention after major CMS updates, plugin installations, API changes, or hosting migrations.
Keep records explaining why exceptions were created and who approved them.
Above all, remember that WAF protection is only one layer of website security.
Secure coding practices, software updates, multifactor authentication, protected backups, and vulnerability management remain essential.
Designing web application firewall rules for managed hosting is about creating effective protection without interrupting the people your website is supposed to serve.
Managed rule collections provide a strong starting point, while targeted custom rules and rate limiting help address application-specific threats.
Equally important is controlling false positives through careful testing, monitoring, and narrowly scoped exceptions.
Remember that rule priorities, provider limitations, and legitimate traffic patterns all influence how well your security policies perform.
A good WAF configuration should evolve alongside your website instead of remaining unchanged after its initial deployment.
Ready to strengthen your hosting security? Start by reviewing your current WAF settings, identifying sensitive endpoints, and testing a few carefully selected rules before enabling broader enforcement.
With the right balance of protection and usability, your website can remain both secure and accessible.